AI Architecture #132
AI governance
original term: AI governance (Eng.) · zarządzanie AI, ład AI, regulacja sztucznej inteligencji
Global-circulation concept — no documented lineage in Central Europe. jump to documentation ↓
Working Definition
AI governance is the ensemble of laws, technical standards, institutional bodies, and organizational procedures that determine who is permitted to build and deploy artificial intelligence systems, under what conditions, who bears legal and financial liability for their harms, and who has the authority to audit compliance. In its narrow corporate sense, the term denotes internal organizational risk management: model registries, pre-deployment impact assessments, red-teaming gates, and clear lines of executive sign-off. In its broad public sense, it encompasses binding statutory legislation (such as the European Union’s AI Act), voluntary risk frameworks and technical standards (NIST AI RMF, ISO/IEC 42001), national AI Safety Institutes, and international treaties. Unlike AI ethics—which asks normative questions about what values a system ought to respect—AI governance is strictly institutional and operational: it asks what enforceable mechanism compels an organization to honor those values when doing so conflicts with speed or profit.
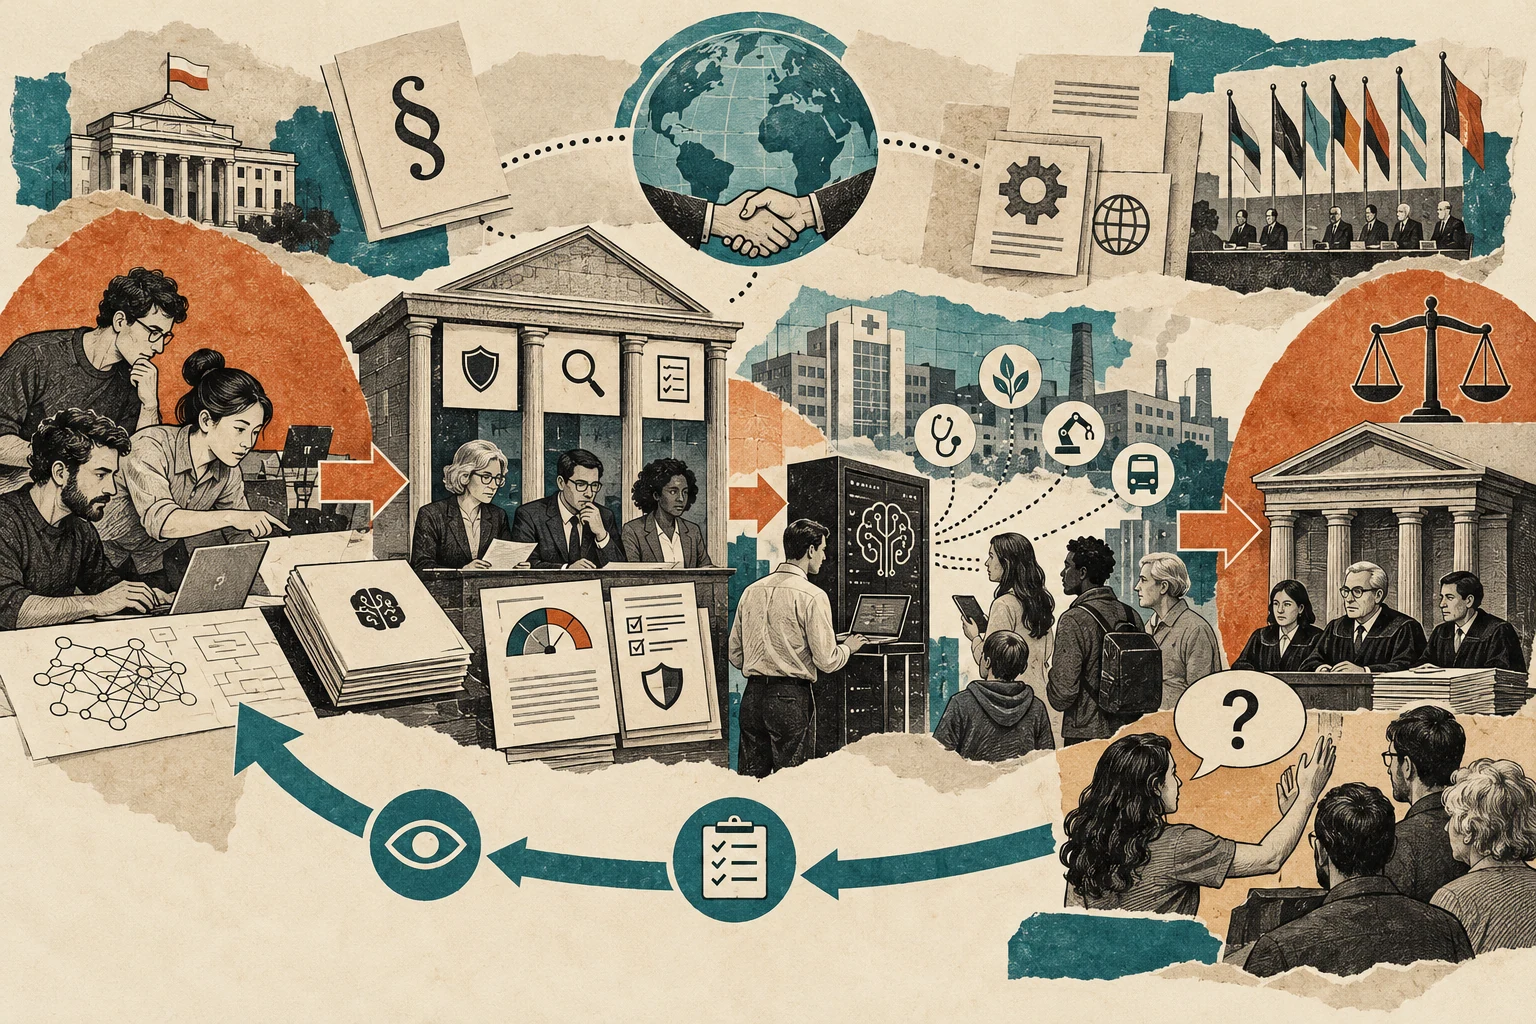
Design, evaluation, deployment, and redress require clear lines of accountability, encompassing people, rules, and institutions around the technology.
AI-assisted illustration · conceptual metaphor View in visual quiz →Genesis and Global Lineage
The concept grew out of two traditions that still speak different languages. The first is postwar technology assessment and product-safety law—epitomized by the U.S. Office of Technology Assessment (1972), David Collingridge’s timing dilemma in The Social Control of Technology (1980), and the EU’s “New Legislative Framework” for product conformity, later cross-fertilized with data-protection law (GDPR, 2016/2018). The second is the Oxford and Bay Area community studying transformative AI risk, where Allan Dafoe published AI Governance: A Research Agenda in August 2018 at Oxford’s Centre for the Governance of AI (GovAI), shifting attention from mathematical alignment toward international relations, compute supply chains, and race dynamics. Between 2016 and 2020, over a hundred non-binding “AI ethics principles” documents (culminating in the 2019 OECD AI Principles and 2021 UNESCO Recommendation) provoked a backlash against toothless “ethics-washing.” The decisive shift from principles to governance occurred between 2021 and 2024: the U.S. National Institute of Standards and Technology released its AI Risk Management Framework (AI RMF 1.0) in January 2023 around four functions (Govern, Map, Measure, Manage), and the European Union enacted the Artificial Intelligence Act (Regulation (EU) 2024/1689), entering into force on August 1, 2024. Meanwhile, management consultancies and software vendors colonized the term to mean enterprise compliance dashboards.
Central European Lineage
We found no documented link between this concept and the intellectual history or historical experience of Central Europe.
We found no documented link between this concept and the intellectual history or historical experience of Central Europe (by our methodology, this means “none found,” not “none exists”; as of October 2026).
Why Now
Between 2018 and 2026, AI governance traveled from seminar paper to binding statute—and then into geopolitical pushback and deregulation. First, ChatGPT’s arrival in November 2022 upended the original drafting premise of the EU AI Act, which had assumed every AI system has a single fixed “intended purpose” (such as sorting résumés); because one General-Purpose AI (GPAI) foundation model powers thousands of downstream uses, EU lawmakers bolted on a separate GPAI regime (and a stricter tier for systemic-risk models above 1025 FLOP) in late 2023. Second, the November 2023 Bletchley Park Summit and President Biden’s Executive Order 14110 (October 2023) established national AI Safety Institutes in the UK, US, and Japan alongside the EU AI Office, institutionalizing state-led pre-deployment evaluation. Third, 2025–2026 shattered the illusion that regulation moves only one way: in January 2025, the incoming U.S. administration revoked EO 14110, pivoted toward American AI dominance, and moved in late 2025 to preempt state-level safety bills, while the February 2025 Paris AI Action Summit shifted focus toward competitiveness. Simultaneously, the Council of Europe opened the first binding international Framework Convention on AI in September 2024, and the EU AI Act entered phased application (prohibitions in February 2025, GPAI obligations in August 2025, high-risk rules in August 2026).
Explanatory Power
The concept separates normative rhetoric from institutional teeth. First, it explains why corporate AI ethics charters (2016–2020) changed almost nothing: they lacked legal addressees, audit trails, and penalties, whereas the EU AI Act and NIST AI RMF assign distinct statutory roles (provider versus deployer), mandate technical documentation (Annex IV), and establish market-surveillance authorities. Second, it clarifies why tech-policy battles revolve around the unit of regulation: regulating downstream applications (credit scoring, biometric categorization, clinical triage) distributes compliance duties across thousands of banks, hospitals, and municipalities, whereas regulating upstream foundation models (via compute thresholds) concentrates oversight on five or six hyperscale labs. Third, it reveals that governance operates through private intermediaries: under the EU AI Act’s product-safety template, statutory phrases like “appropriate levels of accuracy, robustness, and cybersecurity” are translated into engineering rules not by parliaments, but by private European standardization bodies (CEN and CENELEC), third-party “notified bodies,” and liability insurers that effectively define what counts as “safe enough.”
Axes of Debate
Immediate societal harms versus catastrophic frontier risks
Scholars of algorithmic justice and civil liberties (Kate Crawford, Suresh Venkatasubramanian, EDRi) argue that governance must prioritize documented harms from deployed systems: discriminatory welfare and credit scoring, workplace surveillance, copyright extraction, and environmental costs. Frontier-safety researchers counter that general-purpose models capable of assisting in biological weapons design, autonomous cyberattacks, or loss of control pose irreversible public-safety threats requiring upstream licensing and compute governance. Strongest counterargument: Regulating only downstream applications leaves the upstream foundation model untouched—forcing thousands of small deployers to audit a black-box model they did not train, whereas imposing safety obligations at the foundation-model layer addresses shared vulnerabilities at the source. Nature of the dispute: mixed — combining substantive disagreements over capability forecasting with an institutional tug-of-war over the regulatory agenda.
Binding horizontal statutes versus agile voluntary standards and sectoral law
Proponents of the European approach defend horizontal, binding ex-ante legislation (the EU AI Act) to protect fundamental rights before harm occurs. Critics warn from opposite directions: industry voices argue rigid statutes freeze obsolete definitions into law (the Collingridge dilemma), while legal scholars Michael Veale and Frederik Zuiderveen Borgesius show that the AI Act delegates core normative choices to industry-heavy CEN-CENELEC standardization committees, offering less democratic protection than appears. Strongest counterargument: Purely voluntary commitments and ex-post tort lawsuits fail whenever harms are diffuse, opaque, or catastrophic; delegating technical details to harmonized standards marries binding statutory liability with evolving engineering metrics. Nature of the dispute: substantive — concerning institutional delegation and the trade-off between legal certainty and technical adaptability.
The “Brussels Effect” versus regulatory fragmentation and industrial flight
Columbia legal scholar Anu Bradford and EU lawmakers argue that, as with the GDPR, multinationals will adopt European compliance standards globally rather than maintain separate product lines (the Brussels Effect). European startup founders, industrial economists (echoing the 2024 Draghi Report), and U.S. deregulators counter that frontier AI models can easily be withheld or delayed in the EU, and heavy compliance friction after the 2025 U.S. rollback risks turning Europe into a slow-adoption island. Strongest counterargument: No major tech firm permanently abandons a market of 450 million affluent consumers; the real hazard is that complex compliance paperwork acts as a regressive fixed cost that burdens small European AI developers relative to American hyperscalers with large legal teams. Nature of the dispute: mixed — grounded in real trade-offs over fixed compliance costs, but weaponized in lobbying battles.
Underappreciated Angle
AI governance is usually narrated as a two-player drama between the state and the tech corporation, yet its most durable effect is creating a lucrative third estate: the compliance-industrial complex of algorithmic auditors, notified certification bodies, standardization consultants, and “AI governance” SaaS vendors. Because statutory phrases like “mitigating systemic risk” are legally indeterminate, firms achieve safe harbor by purchasing standardized audit certificates from this intermediary layer. As pre-2008 credit rating agencies and carbon-offset verifiers showed, when private auditors are paid by the regulated firm, incentives push toward performative compliance—optimizing paperwork rather than socio-technical risk. Simultaneously, most national market-surveillance authorities across the EU’s twenty-seven member states struggle to recruit machine-learning engineers at civil-service salaries or match the compute needed to stress-test frontier models. Governance on paper without state technical capacity produces a theater of documentation in which regulators audit PDFs written by the regulated firms’ own lawyers.
One-Sentence Takeaway
AI governance is not a philosophical debate over which human values machines ought to respect, but the institutional architecture that determines who can be forced to open their documentation, halt a deployment, or pay damages when those values are violated in practice.
Related Concepts Network
How this concept reinforces, constrains, or complements other analytical frameworks in the corpus. View on graph →
-
AI alignment complements
Alignment attempts to encode human intent and safety constraints into the model weights, whereas AI governance encodes accountability, oversight, and liability into organizations and law; neither can substitute for the other.
-
Frontier AI complements
The dispute over whether to regulate downstream use cases or upstream general-purpose frontier models defines the central architectural cleavage in contemporary AI governance.
-
Goodhart’s law constrains
When formal compliance with a risk-management checklist becomes the institutional target, auditing ends up measuring the completeness of paperwork rather than the actual safety of the deployed system.
-
Moloch and coordination failure reinforces
AI governance institutions are explicitly designed to solve multipolar coordination traps among competing laboratories and states that individually lack incentives to slow down or share safety costs.
-
Algorithmic bias reinforces
The earliest binding AI governance rules and municipal audit mandates emerged directly in response to documented cases of algorithmic discrimination in hiring, credit, welfare, and policing.
-
Explainable AI (XAI) complements
Statutory duties of transparency and meaningful human oversight presuppose that a system’s decisions can be rendered intelligible to human operators—a requirement XAI methods do not always fulfill in practice.
-
Precautionary principle in tension
The tiered, risk-based architecture of the EU AI Act represents a deliberate departure from a strict precautionary ban: outside a narrow list of prohibited practices, systems are permitted onto the market subject to ex-ante conformity assessment.
Reading Canon & Translation Bridge
Foundational texts, introductions, and critical perspectives—with availability of English and Polish editions.
-
foundational text 2023 · English
National Institute of Standards and Technology, Artificial Intelligence Risk Management Framework (AI RMF 1.0), NIST AI 100–1
The voluntary U.S. framework released on January 26, 2023, which structured organizational oversight around four core functions (Govern, Map, Measure, Manage), making “Govern” a cross-cutting institutional function rather than a list of abstract ethical wishes; supplemented in July 2024 by the Generative AI Profile (NIST AI 600–1).
In English: original text written in English
In Polish: no Polish edition
-
foundational text 2024 · English
Parlament Europejski i Rada Unii Europejskiej, Regulation (EU) 2024/1689 laying down harmonised rules on artificial intelligence (Artificial Intelligence Act)
The world’s first comprehensive, legally binding horizontal AI regulation: establishes a four-tier risk pyramid, banned practices, high-risk conformity assessments, a dedicated regime for General-Purpose AI (GPAI) models, and an enforcement architecture (EU AI Office, European Artificial Intelligence Board); entered into force on August 1, 2024, with phased application through 2027.
In English: original text written in English
In Polish: Polish edition not verified
-
foundational text 2018 · English
Allan Dafoe, AI Governance: A Research Agenda
Published on August 27, 2018 by the Centre for the Governance of AI at Oxford, giving the field its academic charter: divides inquiry into the technical landscape, political dynamics, and normative ideal governance for transformative AI.
In English: original text written in English
In Polish: no Polish edition
-
critical perspective 2021 · English
Michael Veale, Frederik Zuiderveen Borgesius, Demystifying the Draft EU Artificial Intelligence Act
A foundational legal critique (“Computer Law Review International” 22/4) showing that the EU AI Act is built on the template of 1980s New Legislative Framework product-safety law—delegating core substantive standards to private standardization bodies rather than creating enforceable individual rights.
In English: original text written in English
In Polish: no Polish edition
-
critical perspective 2023 · English
Anu Bradford, Digital Empires: The Global Battle to Regulate Technology
Compares the three competing global regulatory models—the American market-driven model, the Chinese state-driven model, and the European rights-driven model—offering a sober assessment of the reach and limits of the “Brussels Effect” in AI.
In English: original text written in English
In Polish: Polish edition not verified
-
cross-disciplinary 1980 · English
David Collingridge, The Social Control of Technology
Source of the classic “Collingridge dilemma”: when a technology is young, its social consequences cannot yet be predicted well enough to regulate; by the time the consequences are obvious, the technology is so entrenched that regulation is costly and slow.
In English: original text written in English
In Polish: Polish edition not verified
-
introduction & synthesis 2021 · English
Kate Crawford, Atlas of AI: Power, Politics, and the Planetary Costs of Artificial Intelligence
An accessible yet rigorous mapping of the material, labor, mineral, and geopolitical supply chains of AI that narrow model-centric governance frameworks routinely leave out of view.
In English: original text written in English
In Polish: Polish edition not verified
-
cross-disciplinary 1964 · Polish
Stanisław Lem, Summa technologiae
Chapter IV (“Intellectronics”) poses the question of civilizational steerability once cybernetic decision systems outstrip human comprehension—a philosophical reminder that the problem of governing autonomous socio-technical systems predates modern deep learning.
In English: English edition not verified
In Polish: original text written in Polish